Skip to content
Rekey

Security partner for small teams building with AI

Almost 50% of AI-⁠generated code fails security tests. Was yours written by AI?

Veracode, 2026: AI models wrote code with a known vulnerability in 44% of coding tasks.See the data

I find and fix the security gaps in AI-built apps for small teams. Exposed keys, open database rules, unprotected AI endpoints: fixed, not just reported.

8published CVEs
  • Signed scope before any testing
  • Fixes delivered as pull requests
  • Non-destructive testing
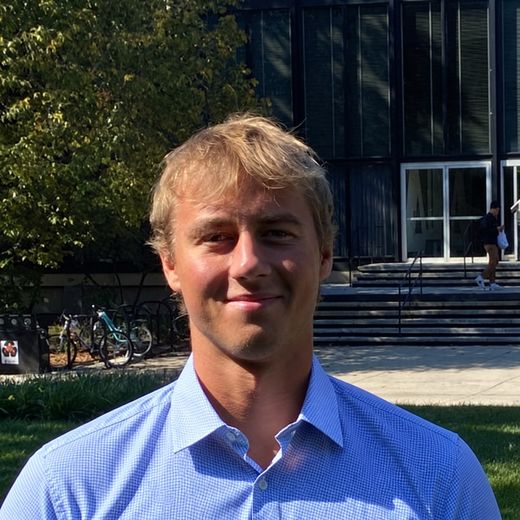
Adrian Korwel

Adrian Korwel · Product security analyst

CriticalExample finding

OpenAI key shipped in the browser bundle

Anyone can copy the key from DevTools and spend on your OpenAI account.

Fix, as a pull request

- VITE_OPENAI_KEY=sk-...+ OPENAI_API_KEY=sk-...   # server only- openai.chat(prompt)     // in browser+ fetch("/api/chat")      // via server
Illustrative example, not from a real client.

I secure apps built and shipped on

  • Lovable
  • Bolt
  • Cursor
  • Replit
  • v0
  • Windsurf
  • Supabase
  • Firebase
  • Vercel
  • Railway
  • Next.js
  • GitHub

Not affiliated with or endorsed by these companies.

The data

It runs. That doesn't mean it's safe.

Veracode gave AI models 80 coding tasks in four languages and checked the code for known vulnerabilities. The code almost always ran. In 44% of tasks, it also shipped a known vulnerability.

44%

of AI code-generation tasks produced code with a known OWASP Top 10 vulnerability.

Average across every model tested. It has barely moved since 2023.

Runs vs. secureAverage pass rate, all models tested
  • Code that compiles99.9%
  • Code that passes security tests56.3%
The best model still fails 1 in 3Security pass rate, Summer 2026 models
  1. GPT-5.5 · OpenAI68%
  2. GPT-5.3-Codex · OpenAI62%
  3. Claude-Opus-4.8 · Anthropic62%
  4. Gemini-3.5-Flash · Google61%
  5. Kimi-K2.6 · Moonshot AI57%
  6. MiMo-V2.5 · Xiaomi53%
  7. Gemini-3-Flash · Google52%
  8. Gemini-3.1-Pro · Google52%
  9. Claude-Opus-4.7 · Anthropic51%
  10. DeepSeek-V4-Flash · DeepSeek51%
  11. Qwen3.7-max · Alibaba50%

Every one of these models writes code that compiles 99 to 100% of the time.

XSS-safe code only 15% of the timeSecurity pass rate by vulnerability type, all models
  • Cryptographic algorithms87%
  • SQL injection83%
  • Cross-site scripting (XSS)15%
  • Log injection12%

Cross-site scripting is a web app bug. It's the kind of code Lovable, Bolt and Cursor write all day.

Source: Veracode, 2026 GenAI Code Security Report. Charts redrawn by Rekey from the published figures.

Read the report (opens in a new tab)

The model won't tell you which half you got.

See how I check and fix it

What I check

The four gaps I check first

They don't show up when you click around your own app, so they ship. Same gaps whether you built with Lovable, Bolt, Cursor or Replit, on Supabase, Firebase, Vercel or Railway.

  1. 01Keys

    Keys in the frontend

    OpenAI, Anthropic, Stripe or Supabase service_role keys bundled into client code or committed to a public repo.

  2. 02Database

    Open database rules

    Supabase tables without row-level security, or Firebase rules that let any signed-in user read and write everything.

  3. 03Secrets

    Secrets everywhere

    The same key copied into .env files, CI settings, mcp.json and laptops, with no plan to rotate it.

  4. 04AI endpoints

    AI endpoints anyone can call

    No auth, no rate limit and no spend cap, so a stranger can run up your AI bill.

Recent examplesOctober 2026

Most small teams still have keys sitting in the same places.

See where to look

Services

Lock it down, then fix what's broken

Two ways to work together, at prices a small team can say yes to. The final price is agreed in writing before anything starts.

Founding clientsMy first 5 clients get 25% off either service, the Lockdown session or Review + Fix, in return for an honest written testimonial I can publish.

  • 01AI Stack Lockdown

    $299one session, flat price

    Book Review + Fix within 30 days and the $299 counts toward it.

    A 90-minute remote session where we lock down your keys and accounts together.

    90-minute remote session

    • Rotate AI and cloud keys
    • Hard spend limits at every AI provider
    • Keys scoped per app and environment
    • Secrets moved out of code
    • 2FA on hosting, GitHub, AI providers and your domain registrar
    • AI dependencies pinned
    • Review of what AI agents and MCP tools can access
    • Access control logic: who can see and change what
    • Short written summary to keep
  • 02Review + Fix

    Includes fixes

    From $699per app

    A security review of your app, delivered as fixes you can merge, not just a list of problems.

    Fixes in pull requests + short report

    • Exposed keys and secrets
    • Supabase RLS / Firebase rules
    • Broken access control
    • Authentication and sessions
    • Payment and API abuse
    • Security headers
    • Every Critical and High finding fixed
    • Medium findings fixed when quick, Low documented with steps
    • Fixes delivered as pull requests you approve
    • One free retest within 30 days

Building apps for clients?

I'll check each client app before it ships. Every app is different, so I quote each one. Ask by email or on a Zoom call, and send me:

  • App name and URL
  • What it does, and roughly how many users it has
  • How it's built (for example Lovable + Supabase)
  • Whether it takes payments or stores personal data
  • When it launches, and how many client apps you want checked

AI Key Lockdown ChecklistFree

The 10 steps I'd work through after a platform tells you to rotate your keys. Do it yourself, at your own pace.

Get the checklist

Weekends and evenings. Not a 24/7 incident response service.

Prices in USD. Testing only begins after a signed scope and written authorization.

How it works

From first call to locked down in four steps

  1. 1

    Free 15-minute call

    We talk through your app, your stack and what worries you. I'll recommend a service, or tell you if the free checklist is enough for now.

  2. 2

    Signed scope and written authorization

    We agree in writing on what's in scope, which environments and accounts are involved, and the price. Nothing is tested before this is signed.

  3. 3

    The work

    A live Lockdown session or a non-destructive review of your app, depending on what you picked.

  4. 4

    Summary and fixes

    You get a short written summary, plus fixes as pull requests you review and approve. Nothing reaches production without you.

I'm a product security analyst and a computer engineering grad student. I look for the kind of gaps AI-built apps tend to ship with: keys in the wrong place, open database rules, and access control that only works in the happy path.

Outside client work I hunt for vulnerabilities in software people depend on, from open-source libraries to desktop apps. Every finding below went through coordinated disclosure and has a public CVE.

When you work with me, you work with me directly, from the first call to the last pull request. Nothing gets handed off.

See my published CVEs

Research

Published vulnerabilities you can check

Real bugs in software people depend on, found and reported through coordinated disclosure. Each one has a public CVE you can check.

8published CVEs

  1. pyasn1pipCo-reportedQuadratic CPU use when decoding constructed BIT STRINGsHighCVE-2026-119196 (opens in a new tab)
  2. pyasn1pipCo-reportedQuadratic-time denial of service in constructed string and indefinite-length ANY decodingHighCVE-2026-119195 (opens in a new tab)
  3. autobahnpippermessage-brotli inflates a whole frame before the message size limit is checkedMediumCVE-2026-116579 (opens in a new tab)
  4. i18next-http-backendnpmQuery-parameter injection through the language value in loadPath and addPathLowCVE-2026-118258 (opens in a new tab)
  5. pypdfpipLong runtimes and large memory use when retrieving form fieldsMediumCVE-2026-113789 (opens in a new tab)
  6. ip-addressnpmZone identifier matched in quadratic time, so one long string can stall the processMediumCVE-2026-111997 (opens in a new tab)
  7. markdown-itnpmQuadratic-time rendering of a multi-line link reference definition (regression since 14.0)HighCVE-2026-111758 (opens in a new tab)
All advisories on GitHub (opens in a new tab)

FAQ

Questions small teams ask

Is this legal? What do you need from me?

Yes, because nothing is tested without your permission. Before any testing, we sign a scope document and you give written authorization listing exactly what I can test. From you I need the app URL, a test account for each user role, and confirmation that you own or control everything in scope. For a Lockdown session we work in your accounts together over screen share, so you never send me your passwords or keys.

Do you need my source code?

Not always. Much of the review works against your running app, the way an attacker would see it. To deliver fixes as pull requests I need access to the repo, and read access to your Supabase or Firebase project lets me check rules properly. We agree on access during scoping.

Will you break my app?

No. Testing is non-destructive: no denial-of-service or load testing, and no deleting or modifying real user data. I use the test accounts you provide, and staging if you have it. Every change goes through a pull request you review and approve.

What if I'm already breached?

Get in touch. I can help you rotate keys and lock down your accounts, usually in a Lockdown session. But I work weekends and evenings and I'm not a 24/7 incident response firm. If customer data is involved or you need help right now, bring in a dedicated incident response provider as well.

What does "fix" actually mean?

Every Critical and High finding gets fixed. Medium findings get fixed when the fix is quick, and otherwise come with clear steps. Low findings are documented with steps, since they carry the least risk. Code fixes arrive as small pull requests, one per issue, each with a plain explanation and how to test it. You review and merge them; I never push to your main branch or deploy. Settings that live in your accounts, like rotating keys, spend caps and 2FA, we change together over screen share. If something needs a bigger rebuild, I write up the problem and a plan, and we agree on it separately.

Do you work with apps that weren't built with AI?

Yes. A hand-written app gets the same review: exposed keys, database rules, access control, auth, payments and API abuse. AI-built apps are my focus, not a requirement.

Contact

Start a conversation, your way

No time for a call? Send an email and we'll take it from there. Prefer to talk? Book 15 minutes on Zoom.

You'll talk to me, Adrian, not a sales team.

Email me

Tell me what you're building and what worries you. I read and answer every email myself.

Write an email

adrian@rekeysecurity.com

Not ready to talk yet?Start with the free checklist